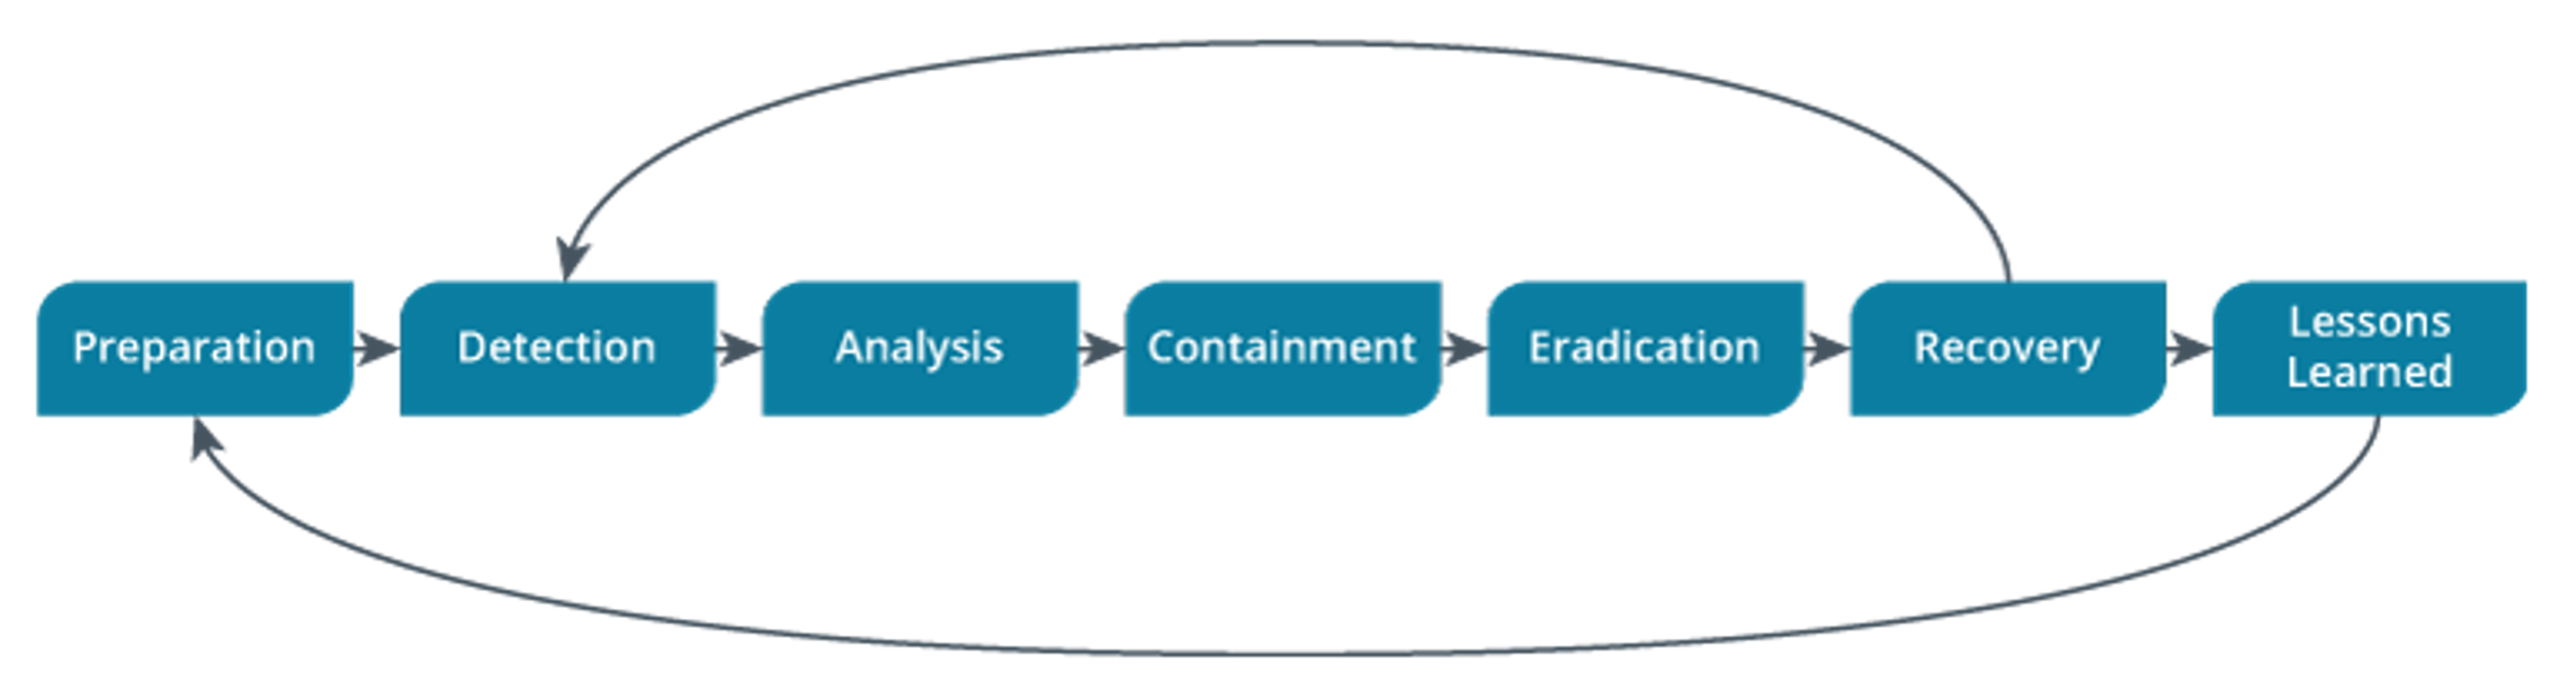
Note! This is different from the NIST and SANS lifecycles - you will be tested on the order of the CompTIA one below!
• Preparation: Build team, tools, playbooks; train staff; establish communication channels
• Detection: Identify anomalies via alerts, logs, user reports; validate true positives
• Analysis: Scope the incident, determine impact, identify IOCs (Indicators of Compromise)
• Containment: Stop the bleeding (isolate systems); short-term (immediate) vs long-term (sustained)
• Eradication: Remove threat (malware deletion, patch vulnerabilities, close backdoors)
• Recovery: Restore systems to production; validate integrity; monitor for recurrence
• Lessons Learned: Post-incident review (debrief); update policies, playbooks, training gaps
• CIRT/CERT: Computer Incident Response Team / Computer Emergency Response Team; core technical responders
• Non-Technical Roles:
– Legal: Breach notification laws, privilege protection, regulatory compliance, litigation hold
– HR: Insider threat discipline, employee support, union considerations
– Public Relations: Media statements, customer communication, reputation management, social media monitoring
• Out-of-Band (OOB) Comms: Separate channels (phone trees, encrypted chat apps, radios) not traversing compromised network; prevents alerting intruder who may monitor email/Slack
• Triage: Rapid categorization (Severity: Critical/High/Med/Low); prioritize business-critical assets
• First Responders: Initial on-scene technicians; secure scene, preserve volatile evidence, document initial observations
• Manual/Physical Inspection: Visual verification of running screens, connected devices, unauthorized hardware; check for data exfiltration in progress
• Responder Fatigue: Alert overload leads to missed critical events; rotate shifts, automate low-value alerts
• Scope: What systems, data, users affected? Timeline of attacker activity
• Impact: Economic (revenue loss), Reputational (customer trust), Operational (downtime), Regulatory (fines)
• Downgrade Low Priority: Filter noise to focus analyst attention on high-fidelity alerts
• Playbooks: Step-by-step response procedures for specific scenarios (ransomware, DDoS, insider threat)
• Runbooks: Technical execution commands (isolate host via EDR, snapshot VM, disable AD account)
• Threat Hunting: Proactive hypothesis-driven search for hidden threats (assumes compromise); IOC sweeps, behavioral analytics; not alert-driven
• Isolation-Based: Disconnect host from network (pull cable, disable switch port, EDR isolation); prevents lateral movement but alerts attacker
• Segmentation-Based: Logical network containment (move to quarantine VLAN, restrict firewall rules); stealthier, maintains connectivity for monitoring
• Documentation: Video everything (screen recording, photographs of setup); timestamped logs of all actions
• Due Process: Legal authority to search/seize; warrant or consent required; maintain chain of custody
• Legal Holds: Preservation order preventing deletion of relevant data; litigation hold notice to custodians
• Write Blockers: Hardware/software preventing writes to source media; preserves evidence integrity (USB, SATA, IDE bridges)
• Hashing: MD5/SHA-256 of original and copy to prove integrity; any change alters hash
• Chain of Custody: Documented trail of evidence possession (who, when, where, what); legal requirement for admissibility
• Tamper-Evident Bags: Sealed storage for drives/devices; shows if accessed
• Faraday Cage: Blocks RF signals; prevents remote wiping of mobile devices via cellular/WiFi/Bluetooth during transport/analysis
• Retrospective Packet Analysis: Reviewing previously captured PCAP for IOCs after discovery
• Metadata Analysis: File creation times (MAC times: Modified/Accessed/Created), EXIF data, author info; detect anti-forensic timestamp manipulation
• Order of Volatility: Capture from most to least volatile:
Quick Distinctions: Kill Chain = attacker progression; IR Lifecycle = defender response; Live acquisition = volatile data but alerts; Static = preserves disk but loses RAM; Chain of custody = legal possession trail; Faraday = signal blocking.